Quick start
Quick start
From zero to a whole team in eight steps.
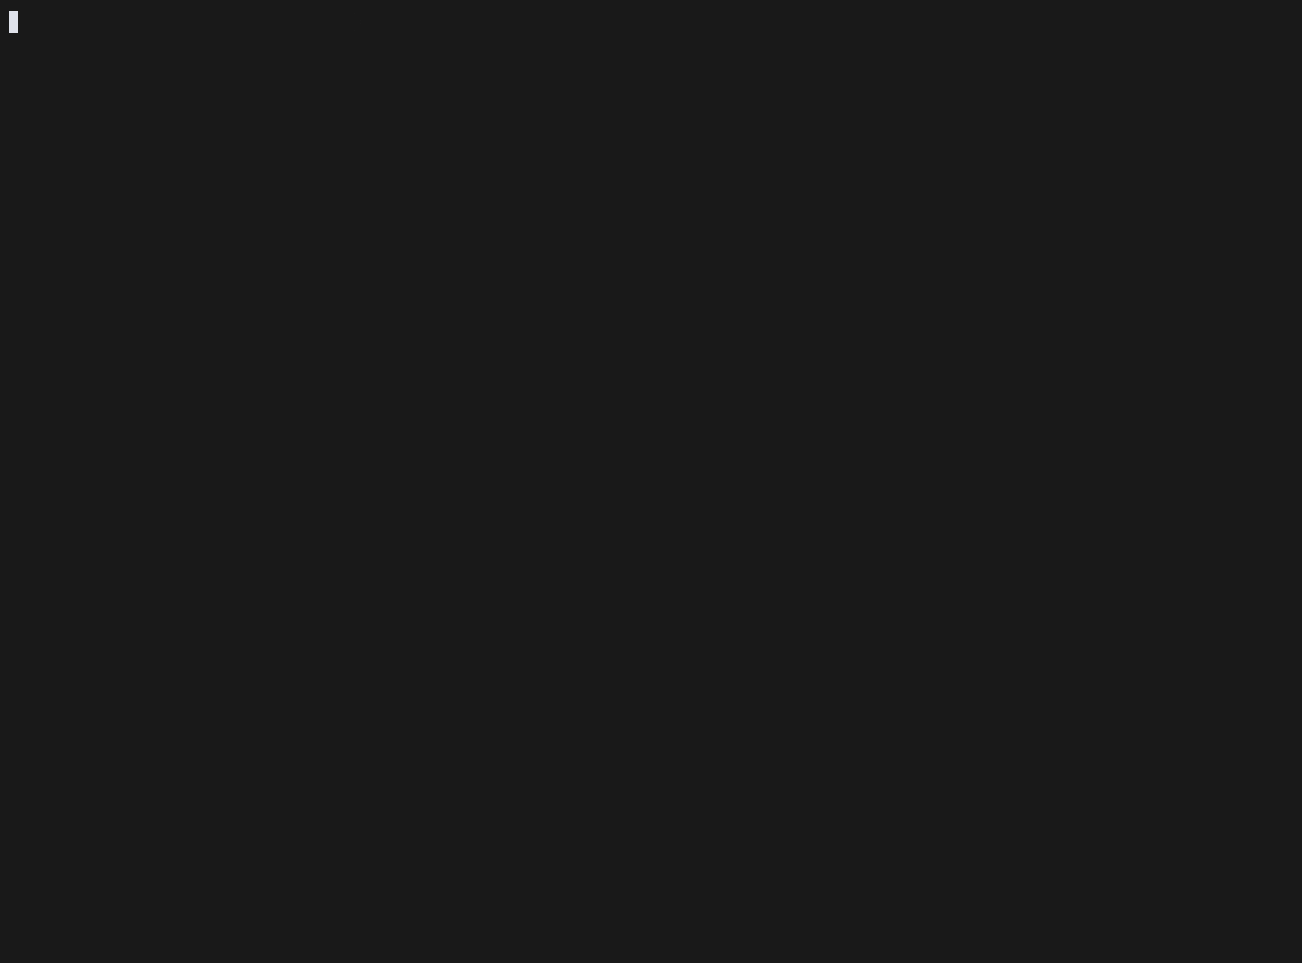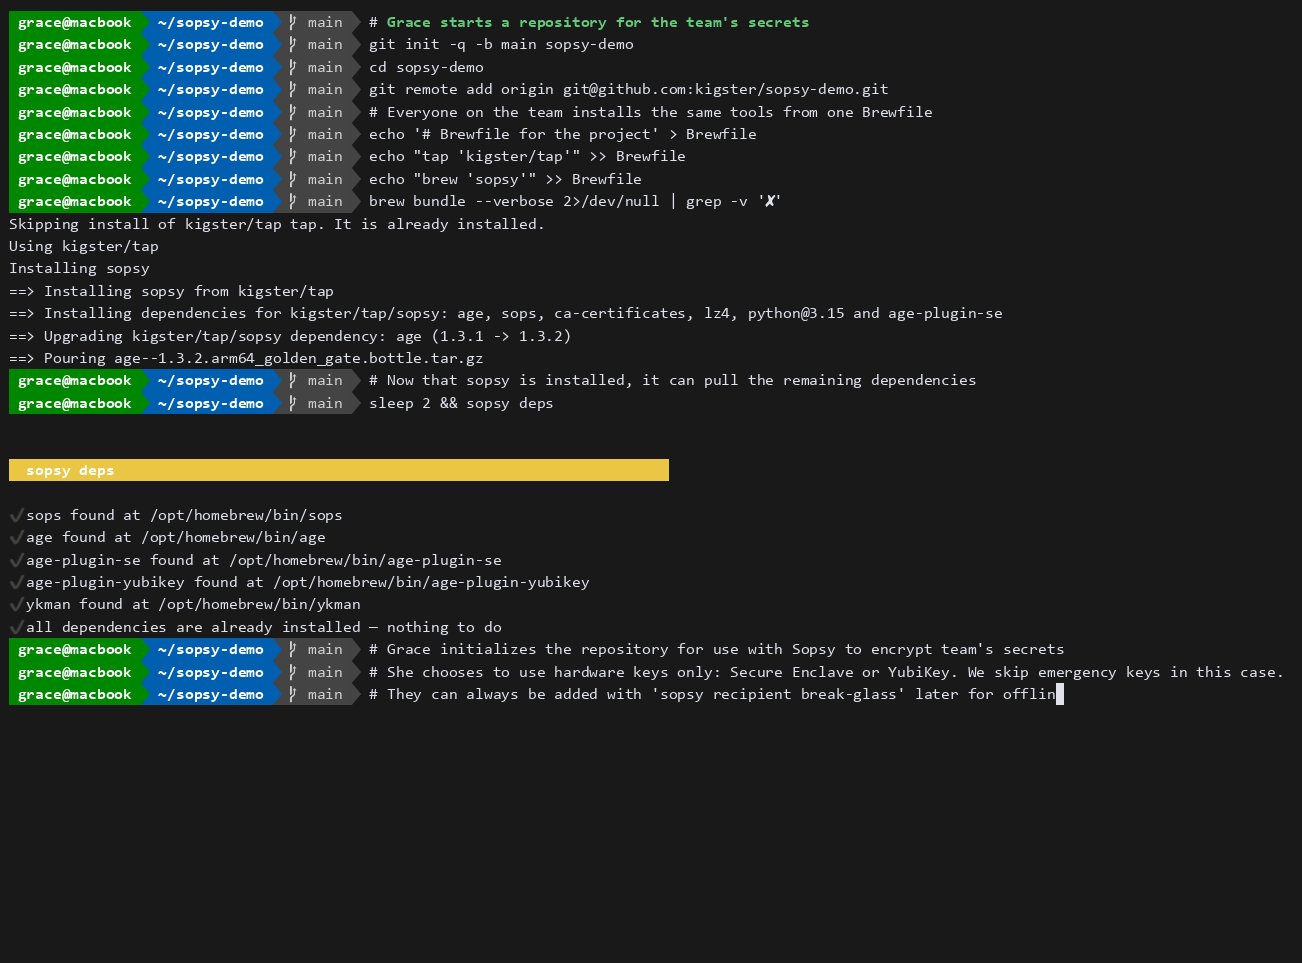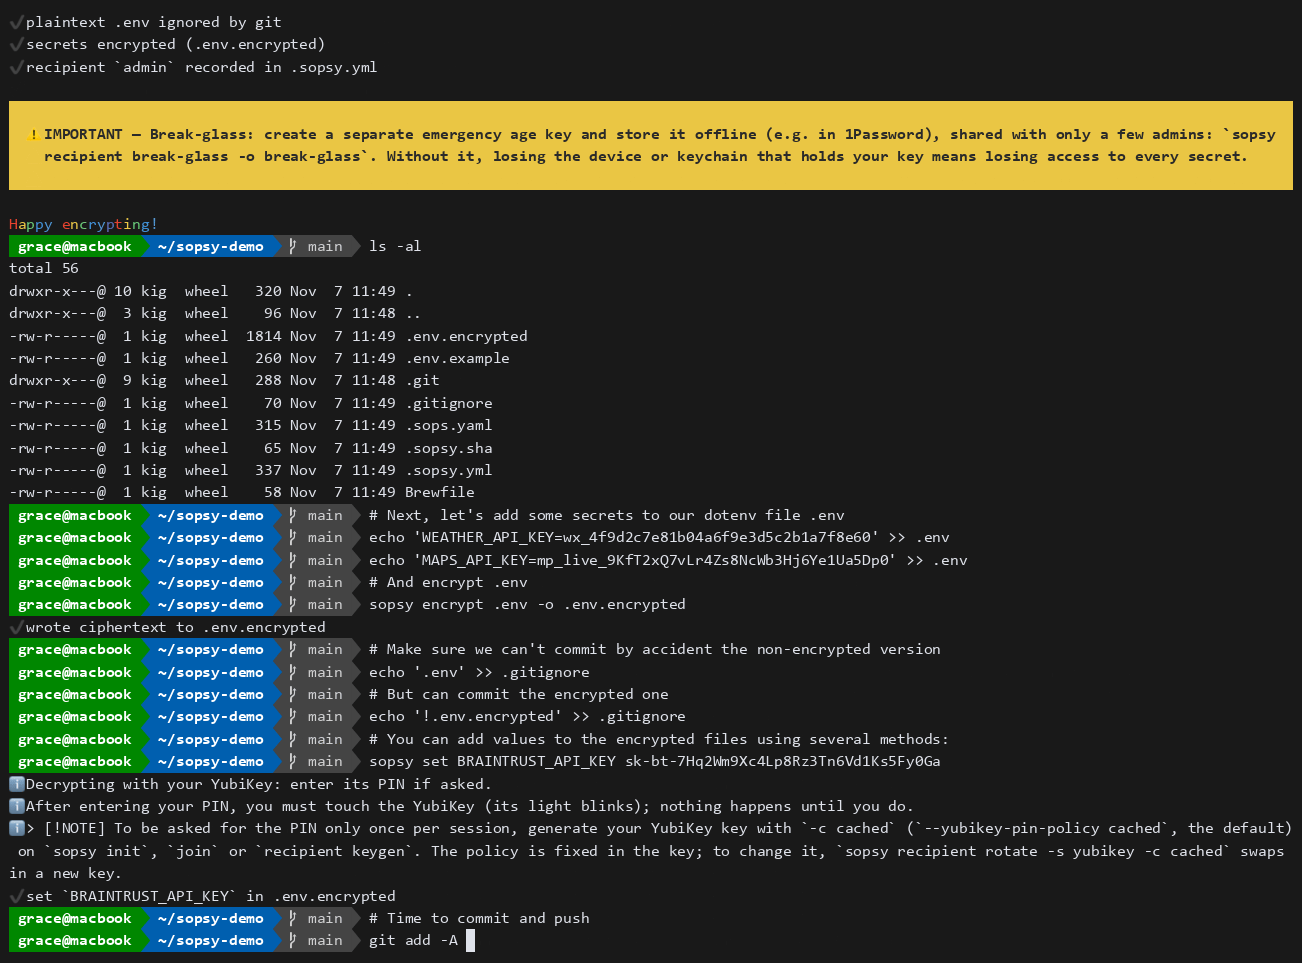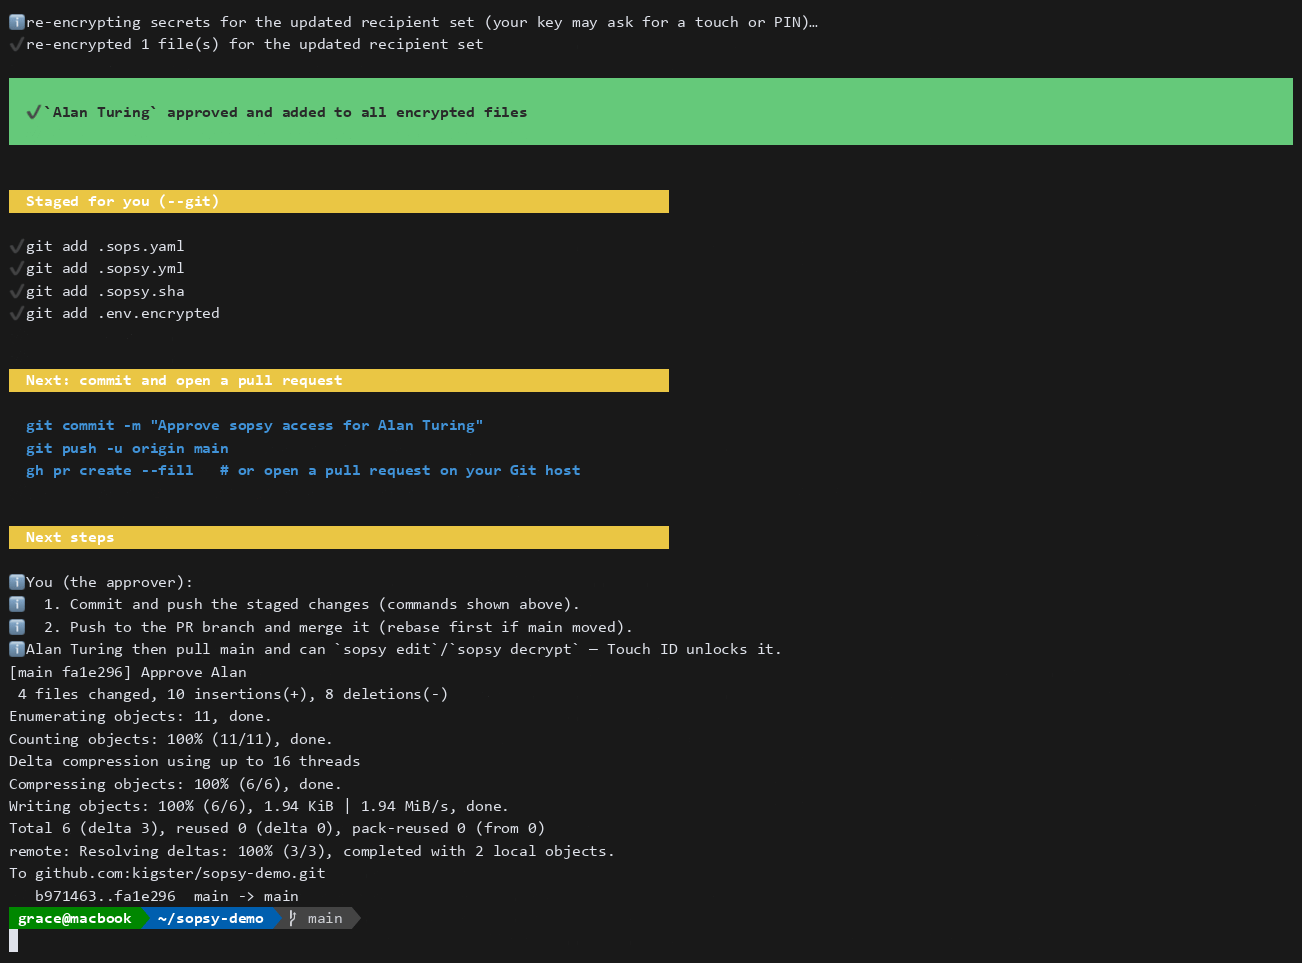
Start (or enter) a git repository
git init my-app && cd my-appBootstrap everything
sopsy init— installs missing tools, records a hardware-only key policy, makes your key in the Secure Enclave or on a YubiKey, writes the config files, and sets up the break-glass key.Put real secrets in
sopsy edit .env.encrypteddecrypts to your editor and re-encrypts on save. Or change one value without an editor:sopsy set API_KEYasks for it with hidden input.Verify hygiene before you commit
sopsy check— the same command your CI runs.Commit the encrypted artifacts
git add .sops.yaml .sopsy.yml .sopsy.sha .env.example .env.encrypted .gitignore— plaintext.envis already gitignored. Push the ciphertext with confidence.A teammate joins (self-service)
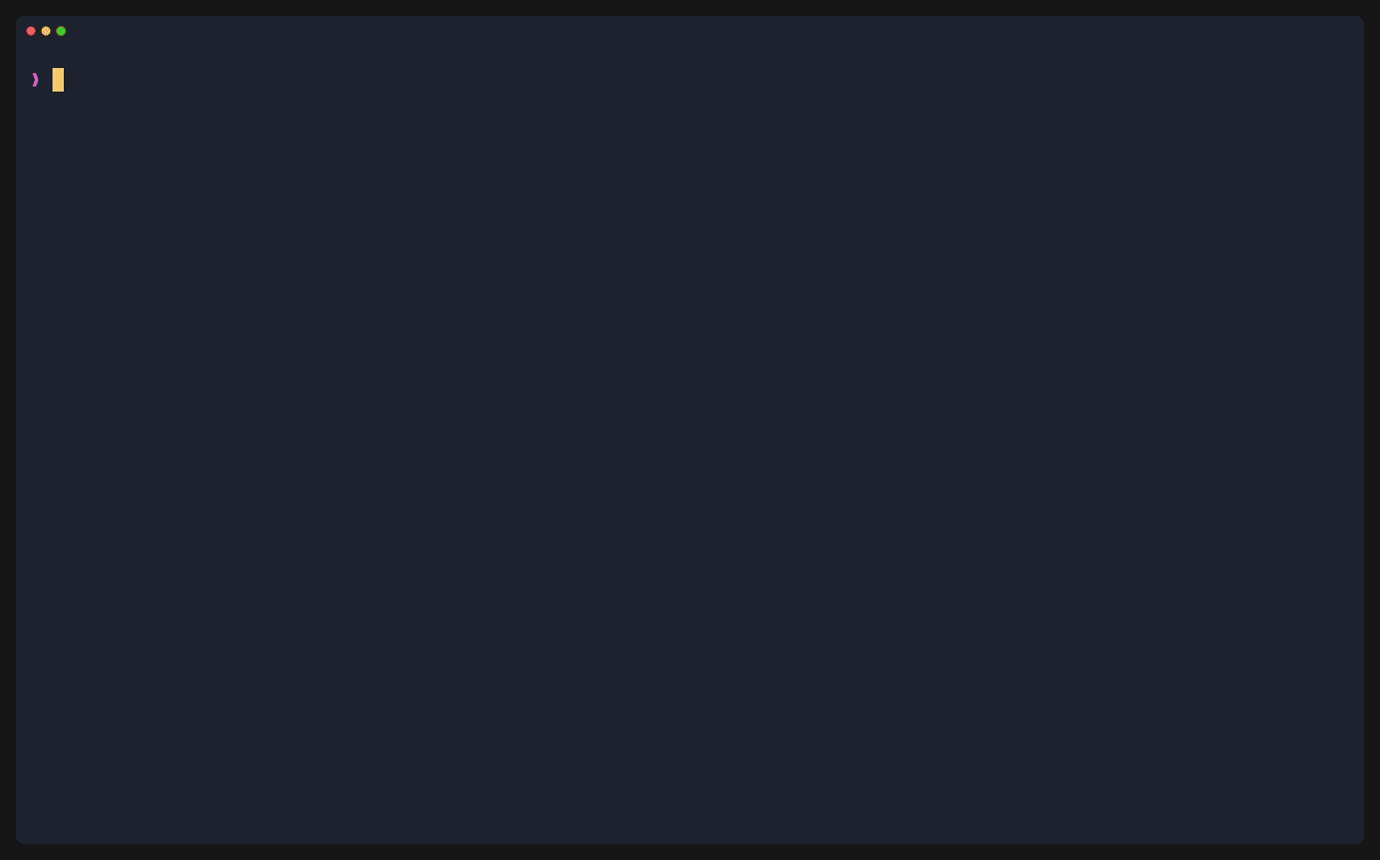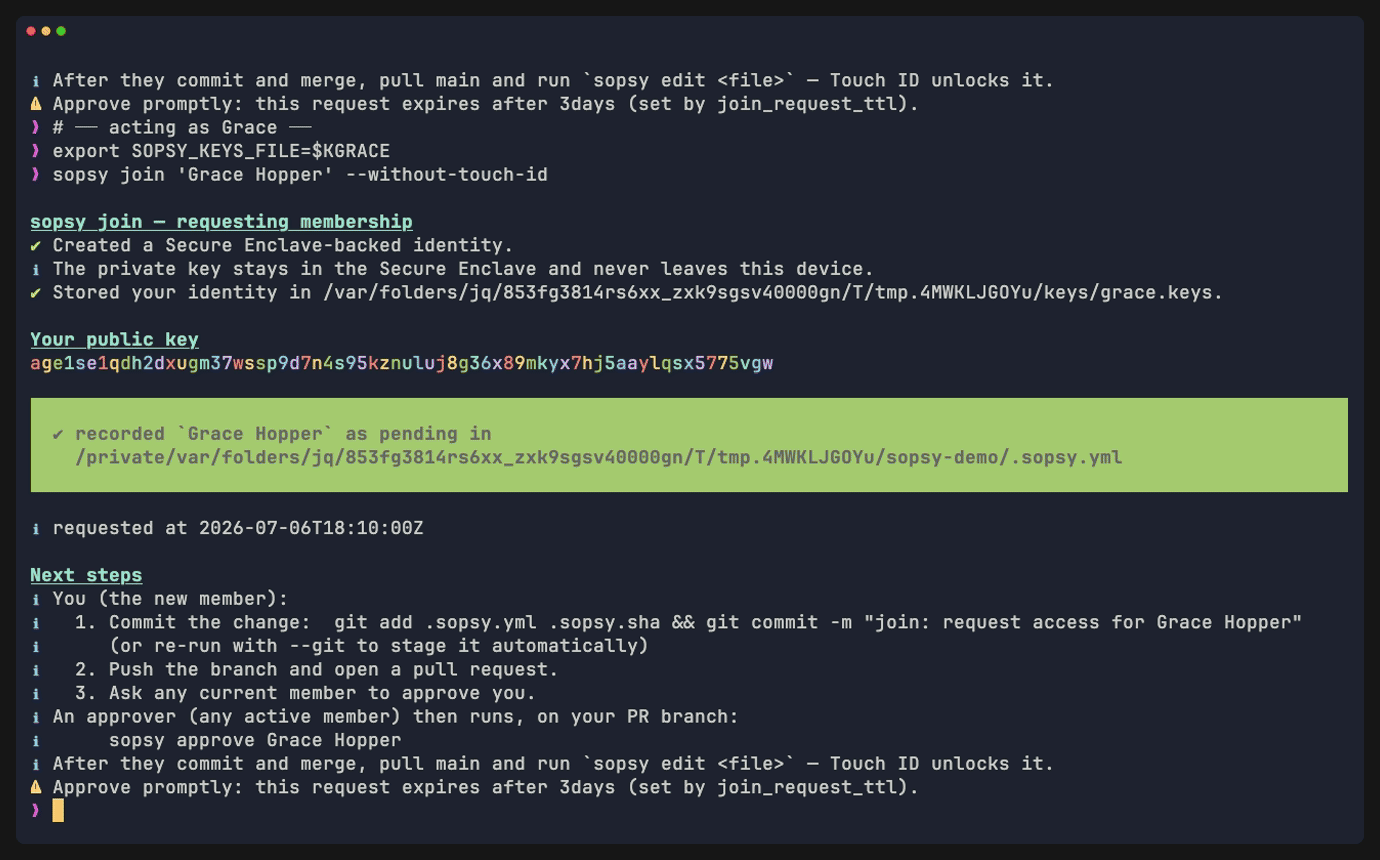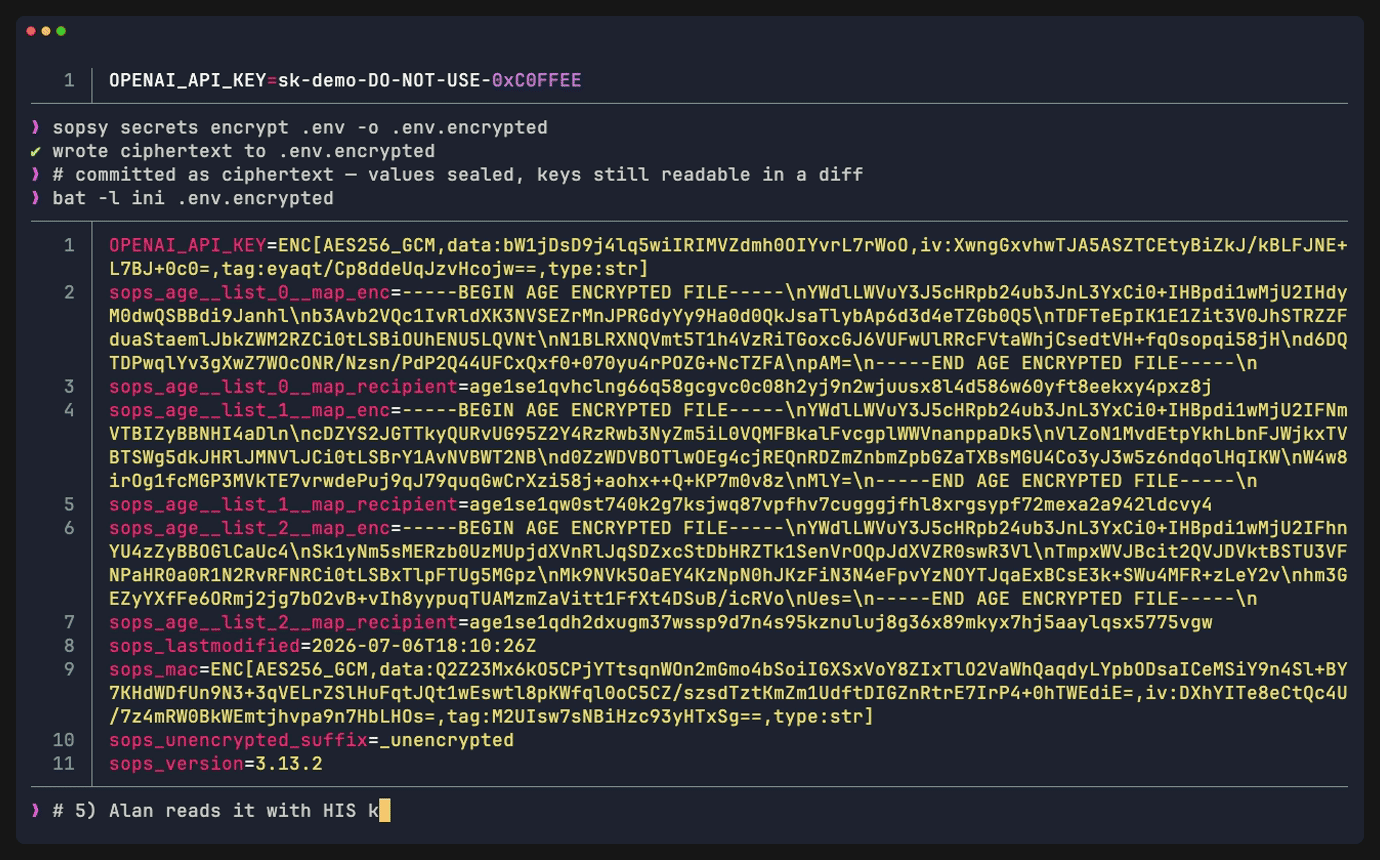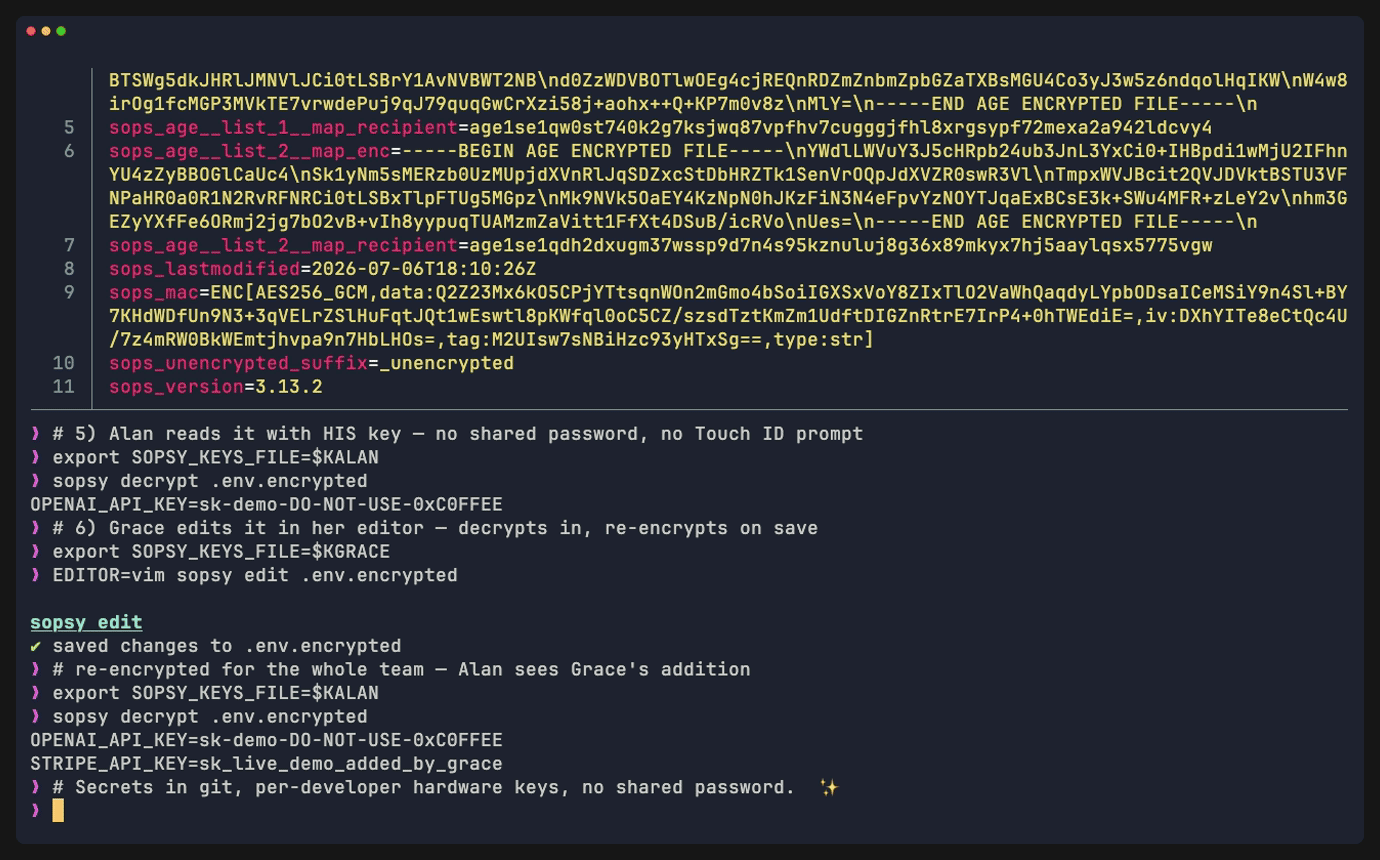
The new dev clones the repo and runs
sopsy join "Alan Turing"— mints their own key in the Secure Enclave or on a YubiKey, within the repository's policy, and records apendingrequest. They commit and open a PR.An existing member approves
Any current member runs
sopsy approve "Alan Turing"— vouches for the key, promotes it into.sops.yaml, and re-keys every secret. Who approved, and when, is recorded in.sopsy.yml—sopsy recipient listshows the whole audit trail. Now Alan can decrypt.Run your app with its secrets
sopsy run -- bin/rails serverdecrypts into that one process's environment. Nothing is written to disk.
Watch the entire process live just below…