sopsyinit[-A stores] [-s store]
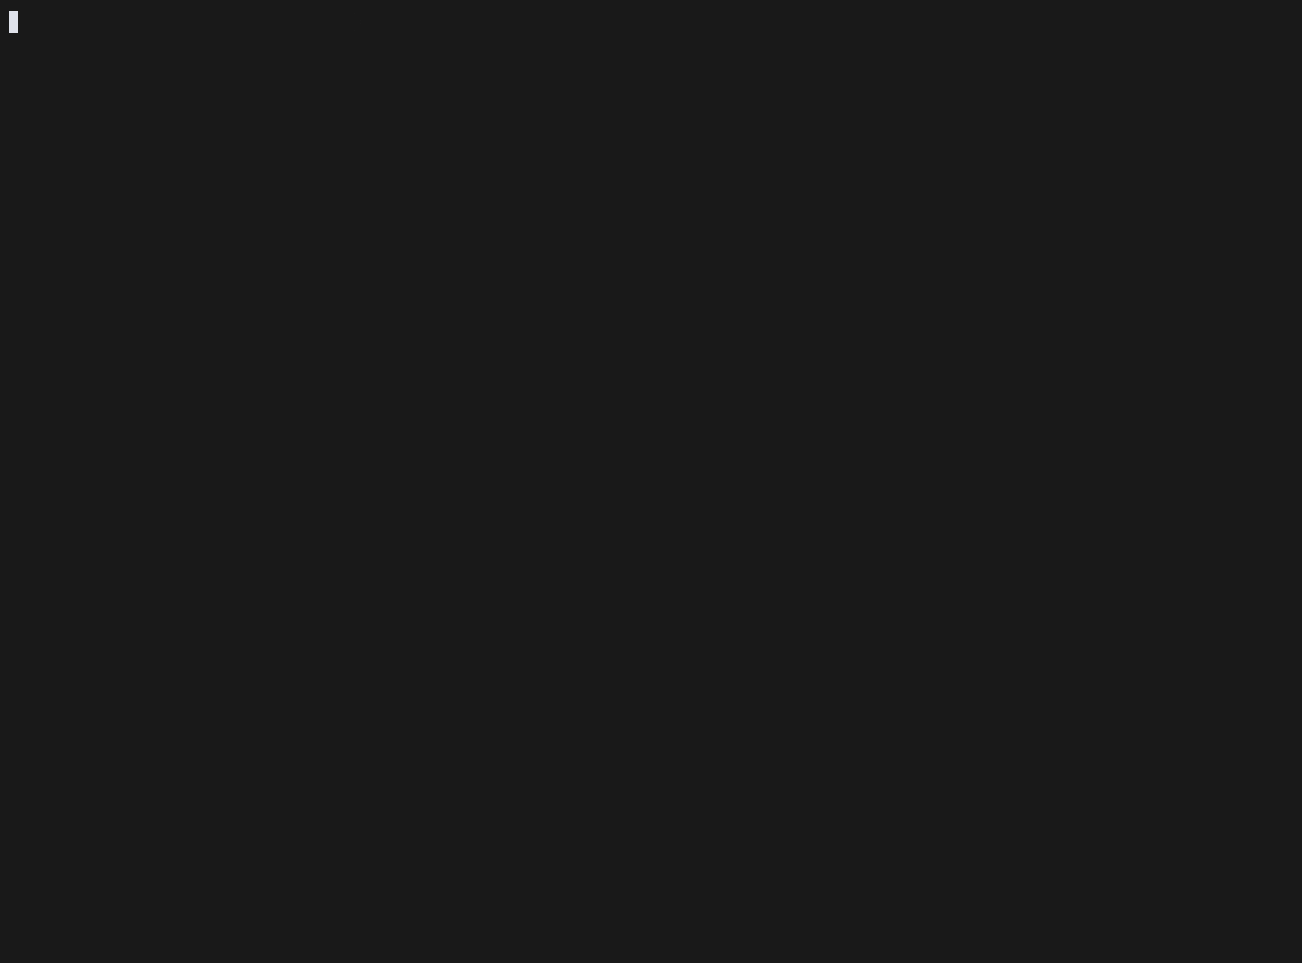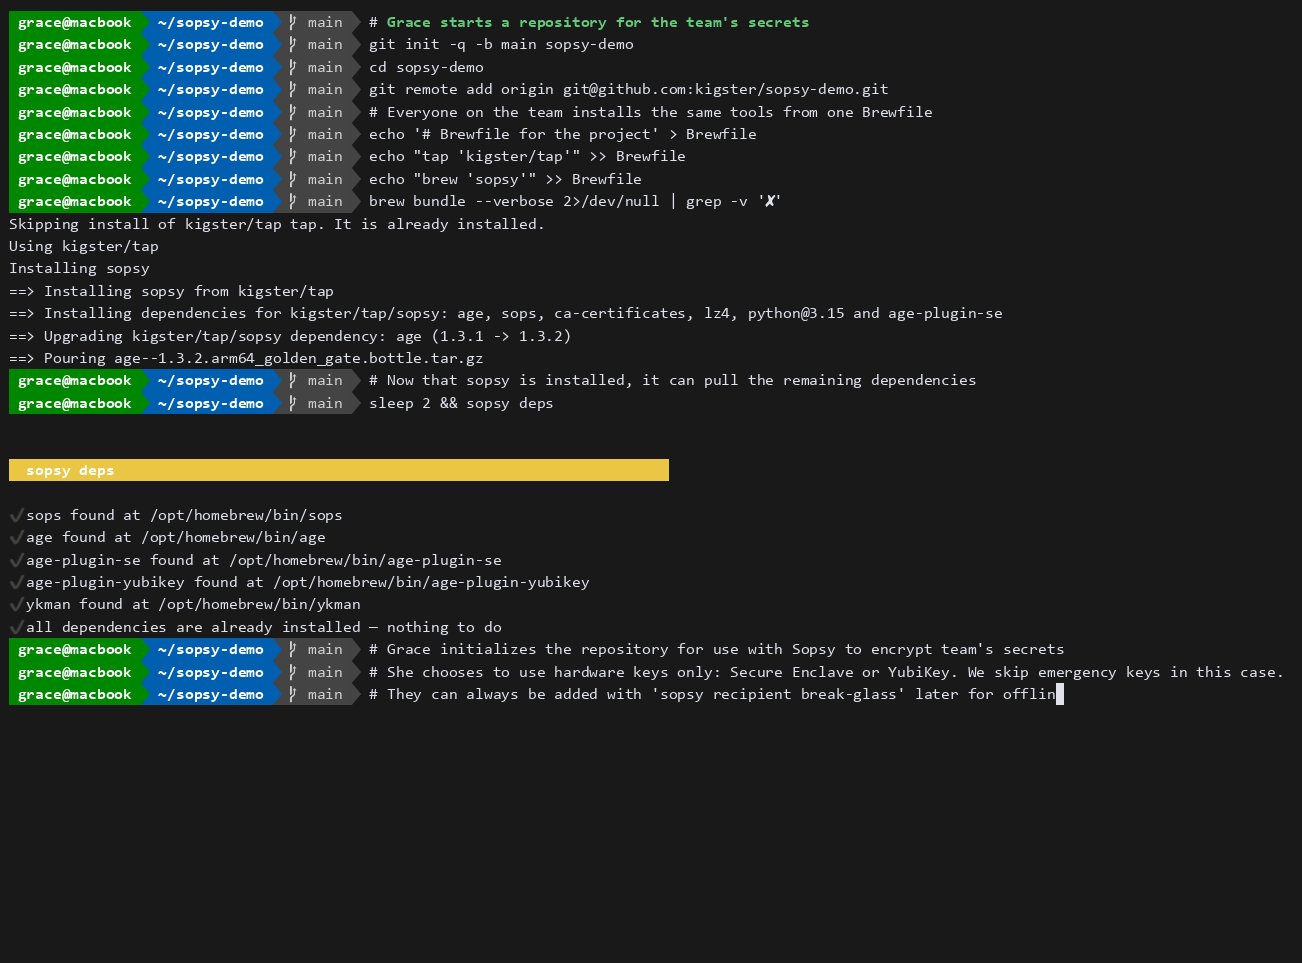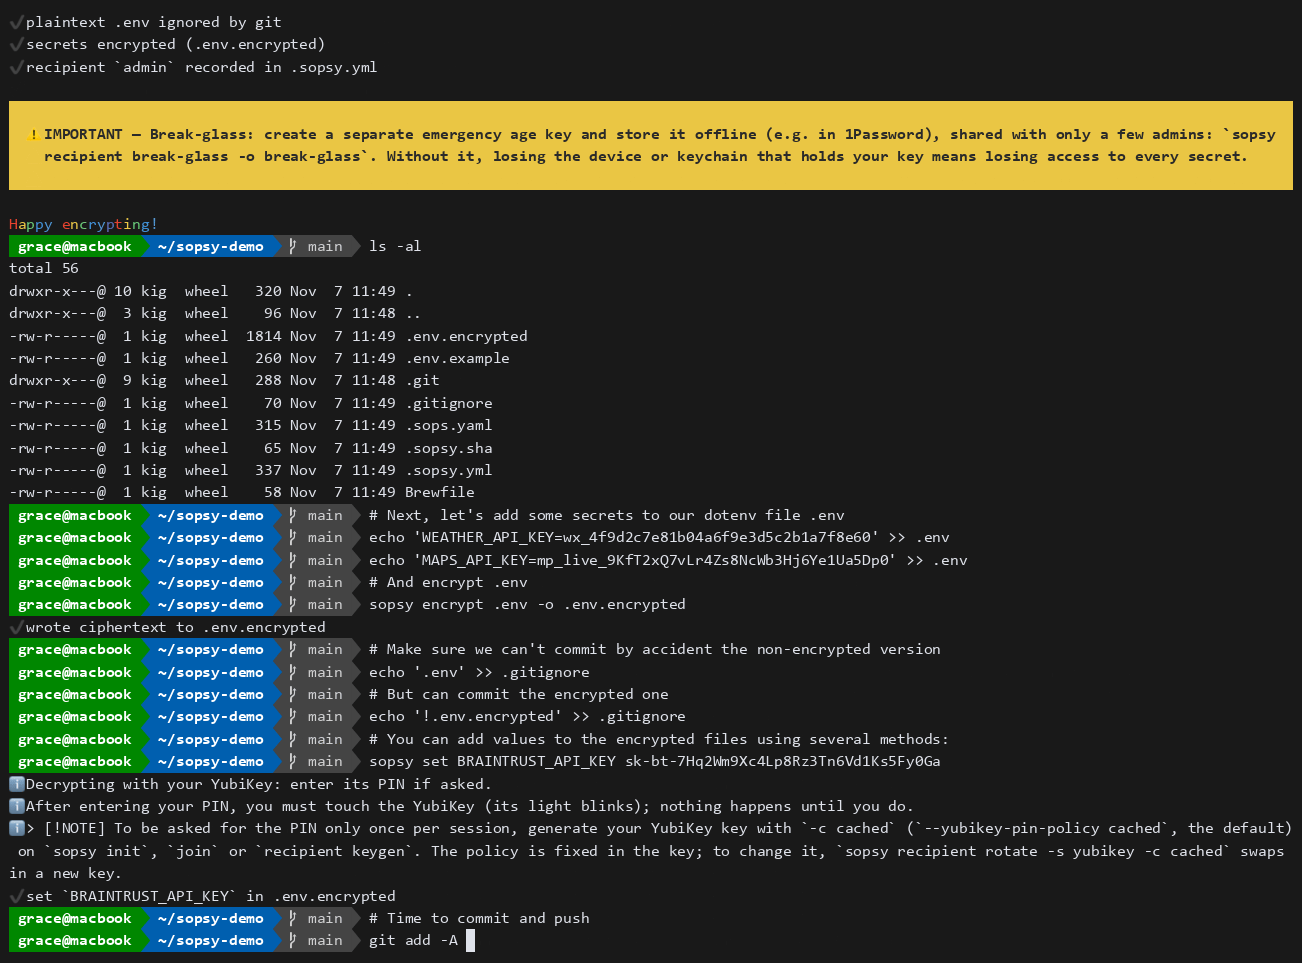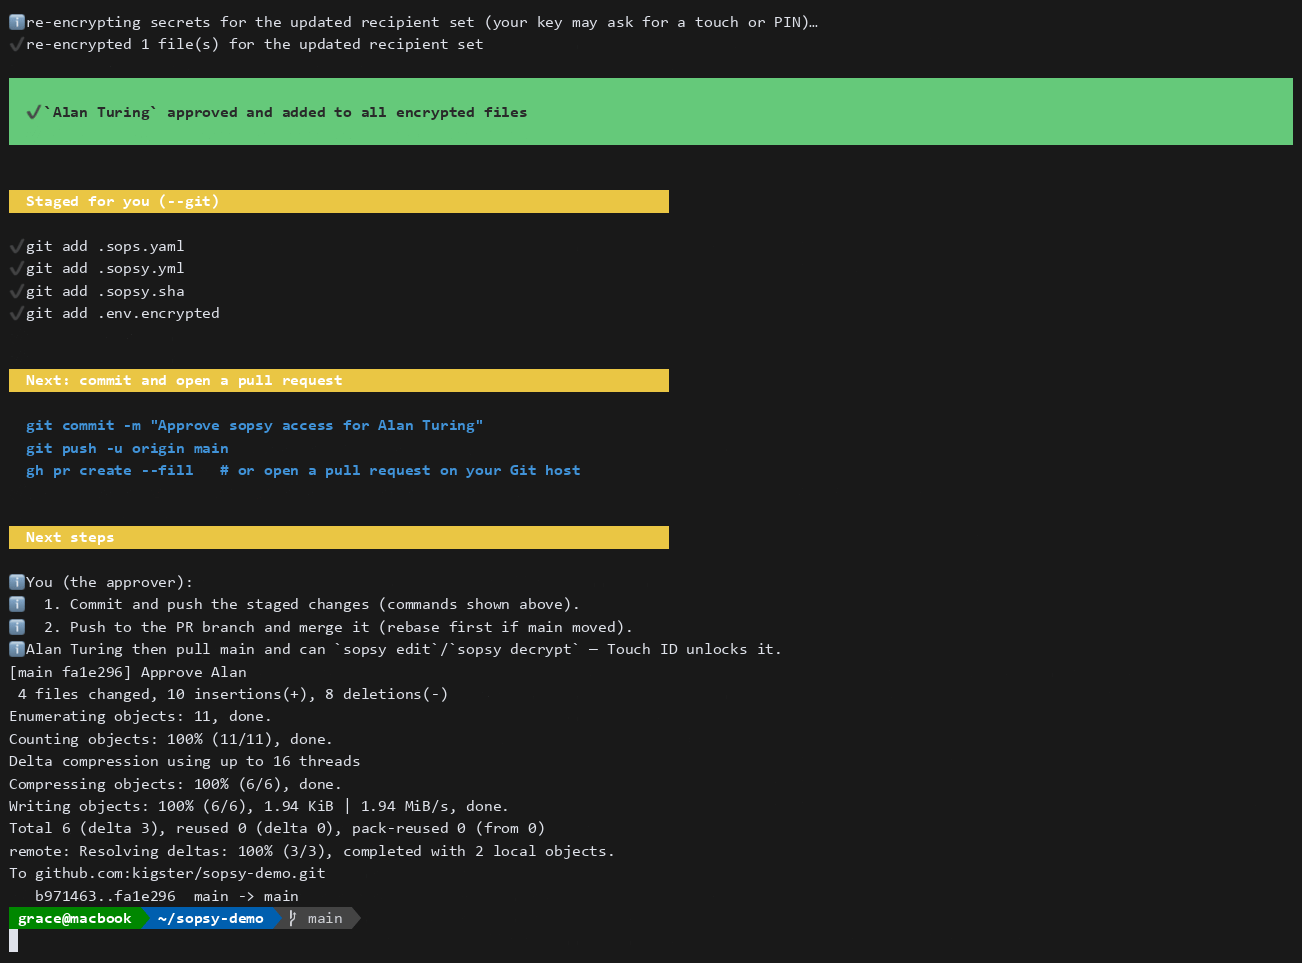
Bootstrap an encrypted repository: install missing tools (--skip-deps to skip), record which key stores members may use (--allow-stores, hardware only by default), make your key, write every config file, and set up the break-glass key (--no-emergency-keys to skip). Idempotent — keeps existing files unless --force.
sopsydoctor
Print a grouped health report — system, tools, repository, recipients — and always exit 0. Repairs a stale .sopsy.sha checksum (its only write). Safe to paste into a bug report.
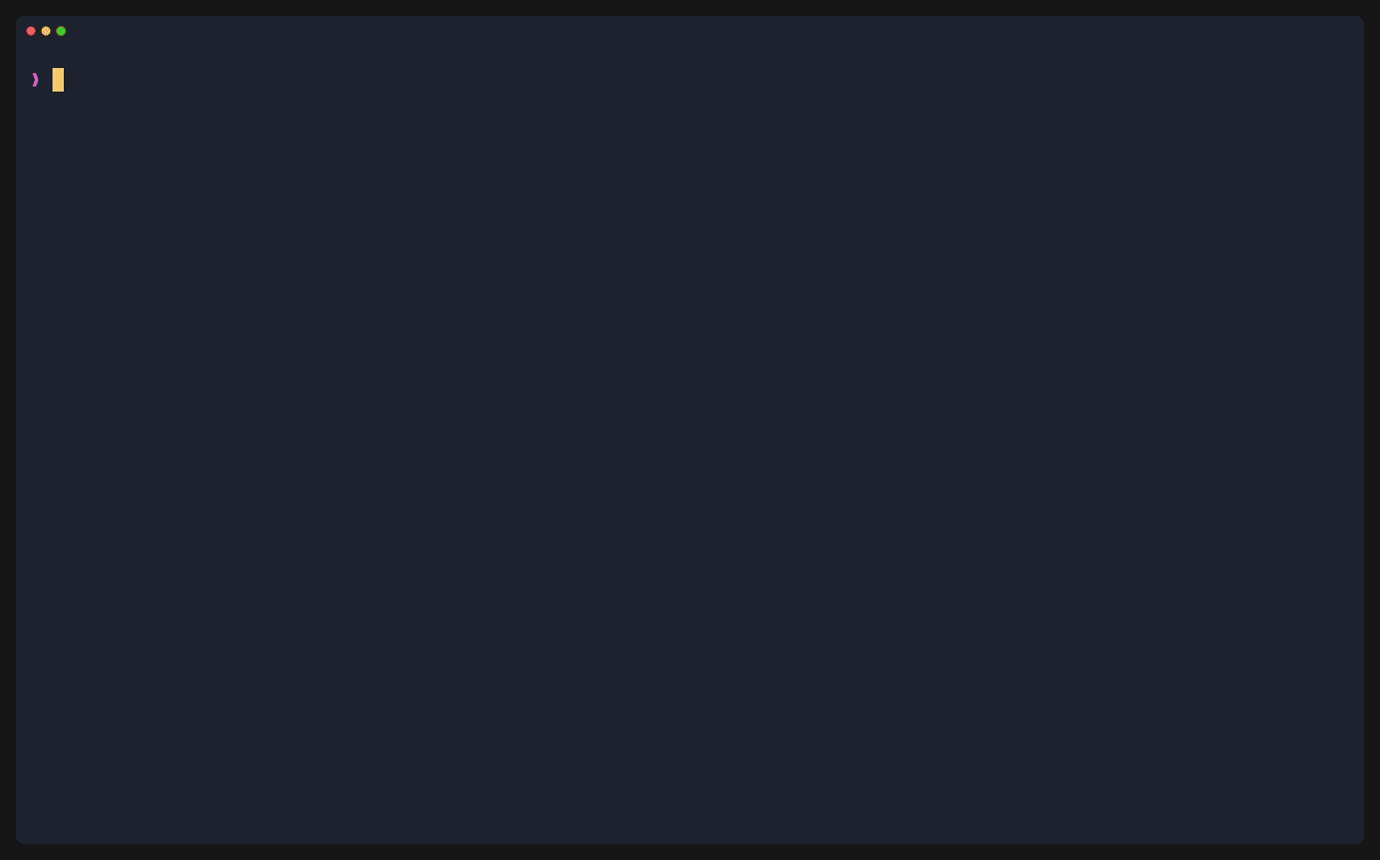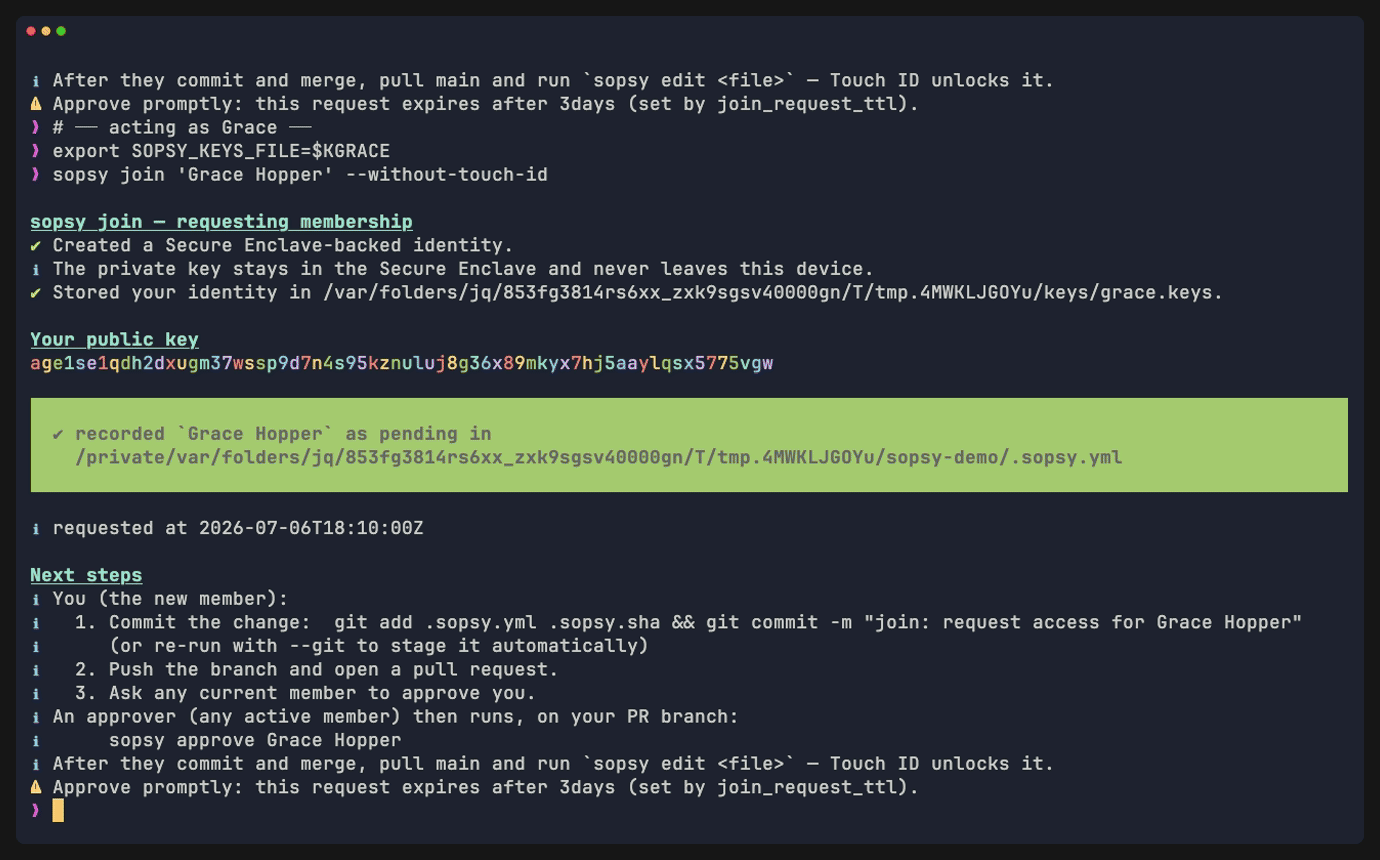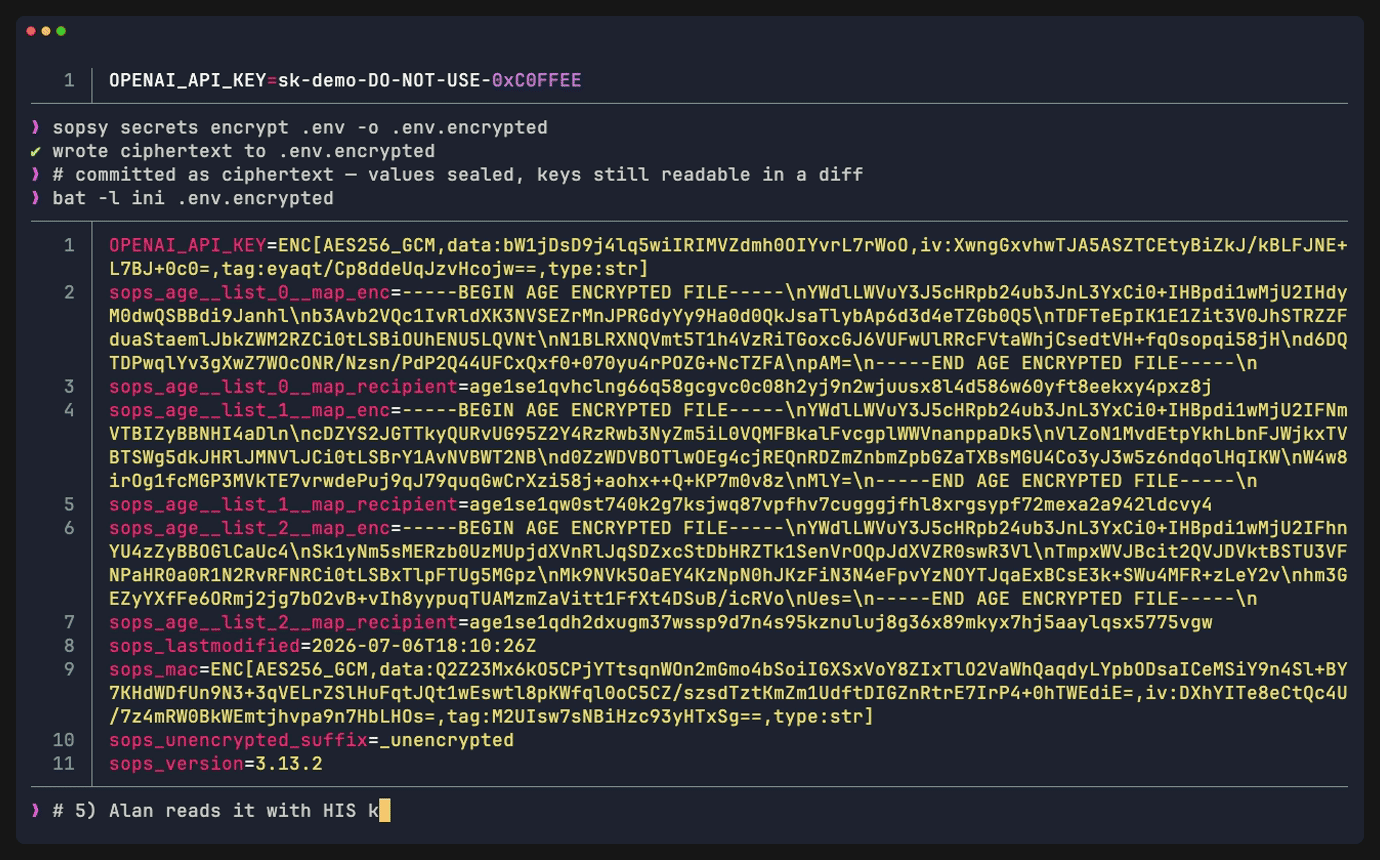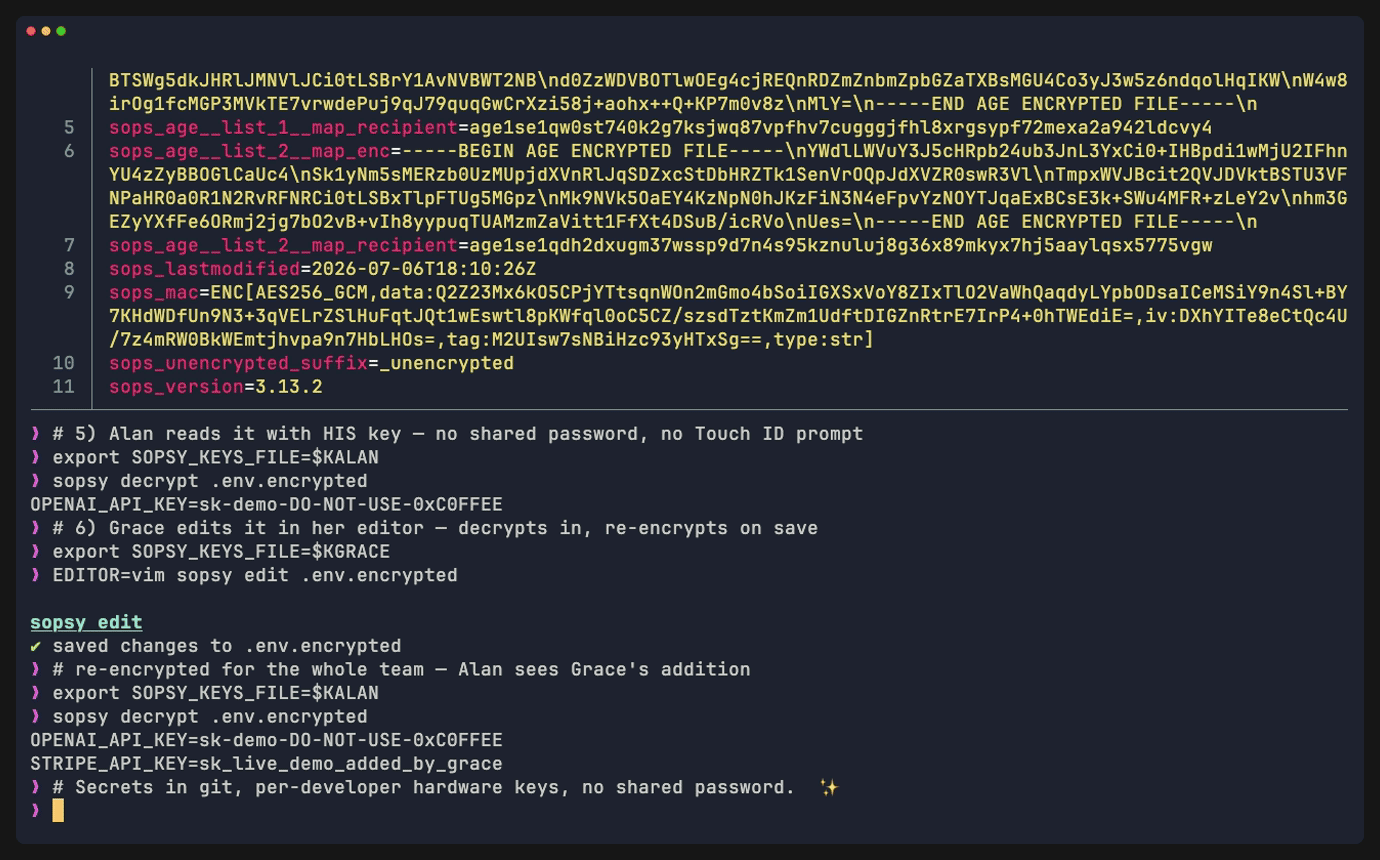
sopsyjoin<name> [-s store] [-t]
Self-service onboarding (alias: request-access): generate your key in any store the repository allows (-s enclave|yubikey|keychain|file) and record a pending request in .sopsy.yml. Commit, open a PR, and ask any member to approve. Pass -t / --without-touch-id to mint the key with no presence gate — handy for direnv and many-window workflows.
sopsyapprove<name>
Any active member vouches for a pending key, promotes it into .sops.yaml, and re-keys every secret — recording approved_by and approved_at for the audit trail, with atomic rollback if the re-key fails. Refuses requests older than join_request_ttl (default 72h).
sopsyedit<file>
Open an encrypted file in your editor through SOPS, with friendly errors and automatic file-type detection. Resolution: --editor → $EDITOR → $VISUAL → vi.
sopsyrecipientadd · remove · list · keygen · rotate · break-glass · ci
Manage who can decrypt. add/remove keep .sopsy.yml and .sops.yaml in sync and re-key secrets; list prints every member with their approval provenance; rotate swaps your key under the same name (--new-data-key also replaces the data key); break-glass and ci run guided portable-key ceremonies; keygen mints a key in any store without registering it.
sopsyencrypt · decrypt<file>
One-shot, scriptable crypto outside the editor. sopsy encrypt writes a .encrypted artifact (or stdout); sopsy decrypt prints plaintext to stdout or -o a file — ideal for direnv and CI. Structured .env/yaml/json/ini encrypt values only; anything else as one blob.
sopsyrun[-f file] -- <cmd>
Run a command with the decrypted values in its environment. Nothing is written to disk; sopsy replaces itself with the command, so exit codes and signals are its own. Repeat -f for several files (later ones win); --pristine passes only the decrypted values.
sopsyset · unset<KEY> [VALUE]
Change one value in an encrypted file without an editor. Omit the value to be asked with hidden input, or pipe it in on stdin; it never appears in a process listing. -f picks the file (default .env.encrypted). set needs sops 3.11 or newer.
sopsyrotate-data-key[files…]
Re-encrypt files under a brand-new data key for the same recipients (sops rotate). With no arguments, every encrypted file the repository manages. Run it after recipient remove.
sopsyyubikey · enclave<plugin args>
Run age-plugin-yubikey or age-plugin-se with your arguments, passed through unchanged. sopsy yubikey --list shows every key on your YubiKey: slot, PIN and touch policy.
sopsytypesalias: list-supported-types
Print the file formats sopsy understands and which extensions auto-detect to each: dotenv, yaml, json, ini (value-encrypted) plus binary (whole-file). Takes no flags; the longer list-supported-types name still works.
sopsycheck
The CI gate: seven hygiene invariants, a pass/fail checklist, non-zero exit on any violation. Never decrypts — needs no key, runs anywhere.
sopsydeps[--check] [--dry-run]
Install the external tools (sops, age, age-plugin-se, age-plugin-yubikey, ykman) with Homebrew. Probes first, installs only what is missing. The remedy that pairs with doctor: --check fails CI if anything is absent, --dry-run previews the brew command.
sopsycompletion<shell>
Generate shell completions for bash, zsh, fish, powershell, and elvish — derived from the CLI definition, so they never drift from the real flags.
sopsy--help· global --git
A clap-based CLI: sopsy --help and sopsy <command> --help are always authoritative. Every interactive prompt has an equivalent flag. The global --git flag stages exactly the files a command changed and prints ready-to-paste commit + PR instructions — a no-op when nothing was modified.